DEPARTMENT OF HOMELAND SECURITY DETAILS RUSSIAN HACKING OPERATION.

WPCNR WASHINGTON WIRE. Special to WPCNR from the Department of Homeland Security. December 31, 2016:

Editor’s Note: The Department of Homeland Security issued this summary of the government investigation of Russian hacking during the American election to the media Friday:

Department of Homeland Security Assistant Secretary for Public Affairs Todd Breasseale issued an executive summary today of the U.S. government’s findings of Russian malicious cyber activity known as Grizzly Steppe.  The executive summary is below.

GRIZZLY STEPPE: Russian Malicious Cyber Activity

Russia’s civilian and military intelligence services engaged in aggressive and sophisticated cyber-enabled operations targeting the U.S. government and its citizens. The U.S. Government refers to this activity as GRIZZLY STEPPE. These cyber operations included spearphishing campaigns targeting government organizations, critical infrastructure entities, think tanks, universities, political organizations, and corporations, and theft of information from these organizations. This stolen information was later publicly released by third parties.

In operations targeting other countries, including U.S. allies and partners, Russian intelligence services (RIS) have undertaken damaging or disruptive cyber-attacks, including on critical infrastructure—in some cases masquerading as third parties or hiding behind false online personas designed to cause the victim to misattribute the source of the attack.

How Do Russian Intelligence Services Operate in Cyberspace?

RIS often uses spearphishing to gain access to targeted systems (see Figure 1 below). In one 2015–16 operation (detailed in our Joint Analysis Report (JAR)), Russian cyber actors conducted a spearphishing campaign to establish presence and persistence on a target network, obtain higher-level privileges, and steal (or “exfiltrate”) information.

These actors tricked recipients into changing their passwords through a fake website that was designed by the Russians cyber actors to appear legitimate. The actors then used those credentials—the username and password—to access the network as if they were legitimate users.

They installed other malicious files, moved freely throughout the target network, gathered data and information, and exfiltrated it from the target network. Russian cyber actors continue to conduct spearphishing campaigns, including one launched as recently as November 2016, just days after the U.S. election.

What is the U.S. Government Doing?

The Department of Homeland Security (DHS) and Federal Bureau of Investigation (FBI) released a Joint Analysis Report (JAR), which provides details of the tools and infrastructure used by Russian intelligence services (RIS) to compromise and exploit networks and infrastructure associated with the recent U.S. election, as well as a range of U.S. government, political, and private sector entities.

The JAR also arms network defenders with the tools they need to identify, detect, and disrupt Russia’s global campaign of malicious cyber activity. We urge users and administrators to use this information to better protect your networks.

What Is Spearphishing?

Spearphishing is the use of forged emails, texts, and other messages to manipulate users into opening malware or malicious software or clicking on malicious links.

Spearphishing attacks can lead to credential theft (e.g., passwords) or may act as an entry point for threat actors into an organization to steal or manipulate data and disrupt operations.

For more information, see the US CERT Tip on Avoiding Social Engineering and Phishing Attacks.

Screenshot of email that states: Incoming eFax: Elections Outcome could be revised [Facts of Elections Fraud]. Sent by Taylor Fax <securefaxsolutions@gmail.com> on Wednesday, November 9, 2016 at 10:39 To undisclosed-recipients. Attachment: election-headlines-FTE2016.docm (1.1 MB). Preview. eFax Solution. You have received a secure message from eFax Solution Corp. Please open the attachment election-headlines-FTE2016 in this email and enter PIN CODE: 3209. SUBJECT: ELECTIONS OUTCOME CUOLD BE REVISED [FACTS OF ELECTIONS FRAUD]. Please note: if you have trouble opening the message, please try the following 1. In your web browser, delete the temporary internet files and cookies. 2. Close the web browser. 3. Open the election-headlines-FTE2016 file in your secure email. End of screenshot.

Figure 1: Sample of Russian Post-Election Spearphishing

Lifecycle of Successful Spearphishing Operation. Starts on the left in Adversary Space, Russian Intelligence Services. Grizzly Steppe 1.) Leverages Operational Infrastructure (Neutral Space, in the middle) 2.) Crafts email with malicious link 3. ) Sent to Recipient (in Victim Space, on the right) 4.) Clicks on link and enters credentials into Website that looks legitimate (in Neutral Space), 5.) Gathers credentials in operational infrastructure, 6.) Uses credentials to Access Targeted System (in Victim Space) 7.) Install malicious files and 8.) Move through targeted systems and 9.) Gather Data of interested which is 10.) Exfiltrated to Operational Infrastructure (in Neutral Space).

Figure 2: Lifecycle of Successful Spearphishing Operation

What Information is in the JAR?

The JAR includes information on computers, servers, and other devices around the world that RIS uses to conduct command-and-control activity between compromised devices, send spearphishing emails, and steal credentials. The JAR identifies these devices by each one’s Internet Protocol (IP) address, which is a set of numbers that serves as an “address” for each computer and is used to transmit data between computers. Because RIS is using other people’s networks without their owners’ knowledge to hide their malicious activity, the computers at these IP addresses typically also host legitimate websites or other Internet services. In some cases, the cybersecurity community was aware of this infrastructure. In other cases, this information has been newly declassified by the U.S. government. The map in Figure 3 shows the 60 countries in which newly declassified IP addresses are located. The JAR also includes information on how RIS typically conducts their activities. This information can help network defenders understand how this adversary operates and can help identify new activity or disrupt ongoing intrusions by RIS.
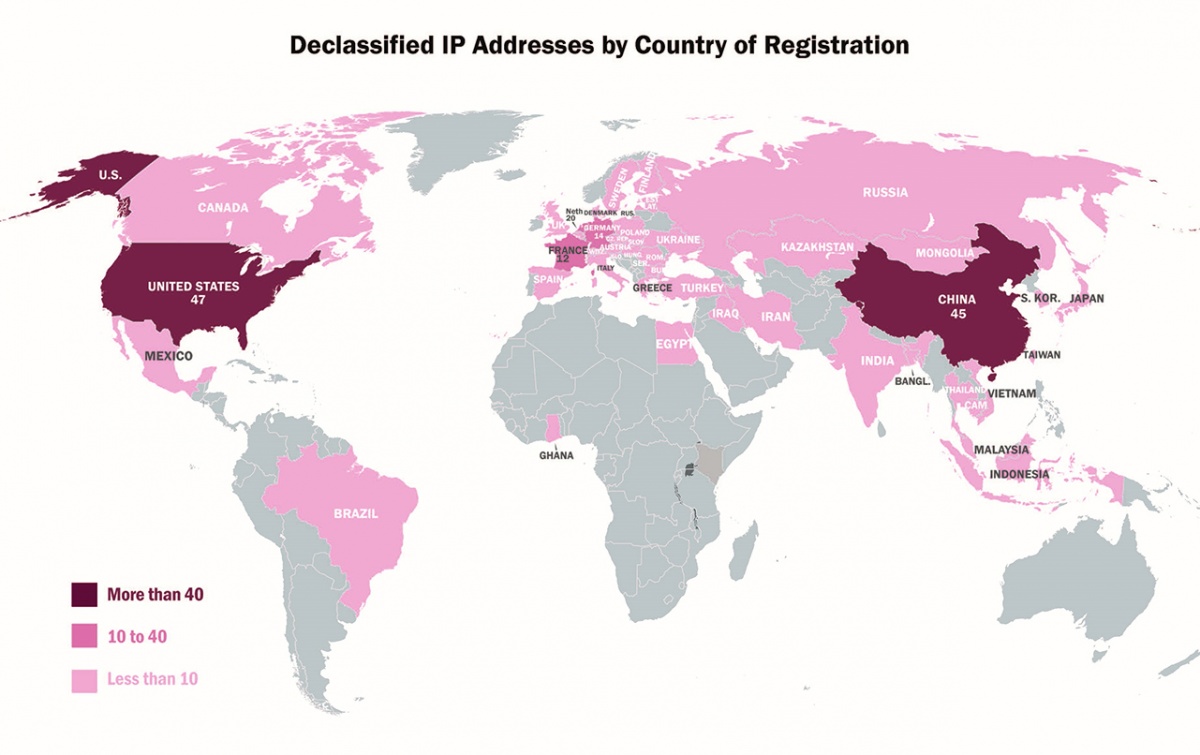
Declassified IP Addresses by Country of Registration. United States: 47. Canada, Mexico, India, Iraq, Egypt, Turkey, Greece, Russia, Kazakhstan, Mongolia, Thailand, Cambodia, Malaysia, Indonesia, Vitenam, South Korea, Japan, Taiwan, Ukraine, Sweden, Finaldn, Poland, Slove, UK, Spaine, Italy, Austria, Poland, and Ghana: Less than 10. France: 12. Germany: 14. Netherlands: 20. China: 45.

Figure 3: Declassified Worldwide Infrastructure Co-Opted by Russian Intelligence Services

How You Can Protect Yourself and Your Networks

A commitment to good cybersecurity and best practices is critical to protecting networks and systems. Here are some questions you may want to ask of your organization to help prevent and mitigate against attacks.

  • Backups: Do we backup all critical information? Are the backups stored offline? Have we tested our ability to revert to backups during an incident?
  • Risk Analysis: Have we conducted a cybersecurity risk analysis of the organization?
  • Staff Training: Have we trained staff on cybersecurity best practices?
  • Vulnerability Scanning and Patching: Have we implemented regular scans of our networks and systems? Do we appropriately patch known system vulnerabilities?
  • Application Whitelisting: Do we allow only approved programs to run on our networks?
  • Incident Response: Do we have an incident response plan? Have we practiced it?
  • Business Continuity: Are we able to sustain business operations without access to certain systems? For how long?
  • Penetration Testing: Have we attempted to hack into our own systems to test the security of our systems and our ability to defend against attacks?

What to Do If You See Signs of Malicious Cyber Activity

If you find signs of malicious cyber activity, we encourage you report it to DHS’s National Cybersecurity and Communications Integration Center ([email protected]or 888-282-0870) or the FBI through your local field office or the FBI’s Cyber Division ([email protected] or 855-292-3937).
Posted in Uncategorized

FEDERAL COURT UPHOLDS MAMARONECK DECISION ON WHICH THE WHITE PLAINS APPEAL OF JUDGE LEFKOWITZ’S VOTE OR ELSE DECISION WAS BASED.

WPCNR THE LETTER TICKER. From the Gedney Association. December 31, 2016: 

(EDITOR’S NOTE: John Sheehan, President of the Gedney Association, long the opposition group to the French American School of New York proposal to build a 7 building campus on the former Ridgeway Country Club alerted the CitizeNetReporter to this legal development:)

“A very significant Federal Court decision was issued recently.  A three judge panel rejected a developer’s claim for monetary damages and found that the Village of Mamaroneck acted within its rights in denying a development proposal for the former Hampshire Country Club and affirmed community opposition as a legitimate factor in the government’s decision.
There are many similarities between the former Hampshire Country Club and the former Ridgeway Country Club. Both:

  • closed during the recent Great Recession;
  • new buyers proposed development: housing on Hampshire and a regional school complex on Ridgeway;
  • required discretionary approvals by elected officials;
  • engendered overwhelming community opposition;
  • proposals were turned down;
  • had the same lawyer filing lawsuits after the proposals were denied;

That’s where the similarities end.

The Village of Mamaroneck remained steadfast in its position defending against its lawsuit and won!  It didn’t cave in to the idle threats of a developer to inflict outrageous monetary damages upon the municipality.

In White Plains, despite a consensus that the City would prevail in its defense of the FASNY suit, the Mayor and three Common Council members (Martin, Kirkpatrick and Smayda) decided to quickly approve an agreement whereby FASNY would put their litigation on hold while the City would review yet another FASNY application.

Importantly, the three Common Council members (Lecouna, Krolian and Hunt-Robinson) who opposed the Hathaway road closure voted against the agreement.   The new agreement is a crude attempt to circumvent the earlier decision when FASNY failed in receiving the requisite super-majority approval.

As a further slap in the face of the record the Mayor and the other three Council members agreed to consider doing an about face on two key earlier decisions by the Common Council that:

  • the entire former Ridgeway Country Club property was an “Environmentally Sensitive Site”;
  • Ridgeway was not to be used as an entrance for FASNY under any circumstances.

In commenting on the recent Mamaroneck Federal court decision the  Mayor  (of Mamaroneck) said:

“One of the most important things about any municipality is zoning because it determines the character of the Village and that’s what just was reinforced in the decision.”

The Mayor’s words are right on target and are typically the cornerstone of public officials everywhere.

Sadly, Mayor Roach and Council members Martin, Kirkpatrick and Smayda have decided for whatever reason not to proceed with their outside attorney’s very strong defense of the FASNY lawsuit.

The Mamaroneck decision demonstrates that municipalities can and must defend against any development that presents a clear threat to the health, safety and welfare of a community regardless of empty threats of monetary damages.

Shortly, another Public Hearing will be scheduled on the FASNY matter.  Please call, write or e-mail our Mayor and elected officials and remind them how Mamaroneck officials acted on behalf of its citizens and that the residents of the south end of White Plains will not succumb to the relentless and aggressive efforts by FASNY to push this unacceptable development upon us.

Best Wishes for the New Year to you and your families.

Regards,

John E. Sheehan, President
Gedney Association

Posted in Uncategorized

WHITE PLAINS WEEK YEAR END REVIEW SHOW–SEE THE WRAPUP OF THE YEAR ON THE INTERNET

2016318wpw 004

JOHN BAILEY, JIM BENEROFE AND PETER KATZ

ENTERING THE 17TH YEAR OF WHITE PLAINS WEEK

COUNTDOWN, STORY BY STORY

THAT WONDERFUL YEAR 2016

35 STORIES IN 30 MINUTES

ON WHITE PLAINS WEEK

THE FASNY FIASCO

THE FASNY “SETTLEMENT”

THE TRANSIT DISTRICT 

THE NEW TAPPAN ZEE BRIDGE

THE NEW WHITE PLAINS MALL

THE NEW GALLERIA MALL

THE NEW GOOD COUNSEL PROPOSAL

THE YEAR HILLARY CAME TO TOWN

THE YEAR OF THREE SCHOOL SUPERINTENDENTS

THE TERRIBLE TEST SCORES

THE LOWEST CITY AND SCHOOL BUDGET INCREASES IN 15 YEARS

HOW COME WESTCHESTER COUNTY CAN’T ADD–THEY NEED A NEW CRYSTAL BALL

PSST! HEY MACK–WANNA RUN AN AIRPORT? JUST GIVE US $15 MILLION TO BALANCE OUR BUDGET

WHAT’S NEXT? DO YOU REALLY WANT TO KNOW?

AND MORE

ON

THE WHITE PLAINS WEEK TRADITIONAL YEAR END REVIEW SHOW

SEE IT INSTANTLY ON YOU TUBE AT

OR
OR
www.wpcommunitymedia.org
Posted in Uncategorized

Celebrate New Years Eve in White Plains NY USA in Downtown White Plains

WPCNR MAIN STREET JOURNAL. From The Mayors’ Office.

The City of White Plains and the White Plains BID are once again preparing to ring in the New Year at our downtown New Year’s Eve Spectacular.

2015101newyears 020The event is held at the intersection of Main and Court Streets and includes a DJ as well as a live band, a crowd countdown and ball drop, followed by a not-to-be-missed fireworks display and confetti.

The event is large and a number of street closures are necessary. The attached map of downtown White Plains highlights the street closings as well as parking options for attendees. The City will begin closing streets in the event area at 1:00 p.m. on New Year’s Eve. Streets will begin to re-open to vehicular traffic after the event is over, starting at approximately 1:00 a.m.

The event will be accessible via gated entry only. Four gates will be set up at the following locations:
– Main Street at Church Street – Renaissance Square at Williams Street
– Court Street at Martine Avenue – Martine Avenue at Mamaroneck Avenue

Please note: No large bags will be permitted inside the event area and all bags are subject to search at the entry gates.

We ask that all attendees plan ahead, leaving extra time to go through security before entering the event. In addition, the event will be a No Fly Zone for Unmanned Aerial Vehicles (aka “drones”). These security precautions are intended for the safety of the public attending this event.

New Year. Safe Ride.

We are pleased to announce that for the 13th consecutive year, Heineken USA is partnering with the City of White Plains and the White Plains Business Improvement District on its New Year. Safe Ride. program, created to help local residents get home safely on New Year’s Eve. Over the past 12 years, the program has provided free and safe rides home to approximately 4,500 Westchester County residents of legal drinking age.

Through the New Year. Safe Ride. program, HEINEKEN USA will provide free and safe rides home for Westchester County residents of legal drinking age who celebrate New Year’s Eve in downtown White Plains. Between 11:00 p.m. on December 31 and 3:00 a.m. on January 1, a dedicated fleet of 30 cars will provide complimentary rides home for those 21 and older traveling from the heart of downtown White Plains to anywhere in White Plains or across Westchester County.

The Safe Ride pick-up location will be located on the corner of East Post Road and Mamaroneck Avenue.

The White Plains New Year’s Eve Spectacular promises to be a fun, family-friendly event. All are encouraged to come downtown and ring in the New Year close to home with us in White Plains.

Posted in Uncategorized